
CISO as a Service
As part of our CISO as a Service (Chief Information Security Officer) offering, we’ll help you manage the tasks associated with NIS2, DORA, CRA, and other regulations.
CISO as a Service
An experienced external CISO, along with a team of experts, will take charge of your cybersecurity.
Governance, compliance, risk and supplier management, incidents, and support during audits and inspections.
Focus on the Cybersecurity Act (ZKB), DORA, ISO 27001, and preparing manufacturers for the CRA.
An external CISO serves as the cybersecurity manager in accordance with the ZKB.
+
The cybreg platform
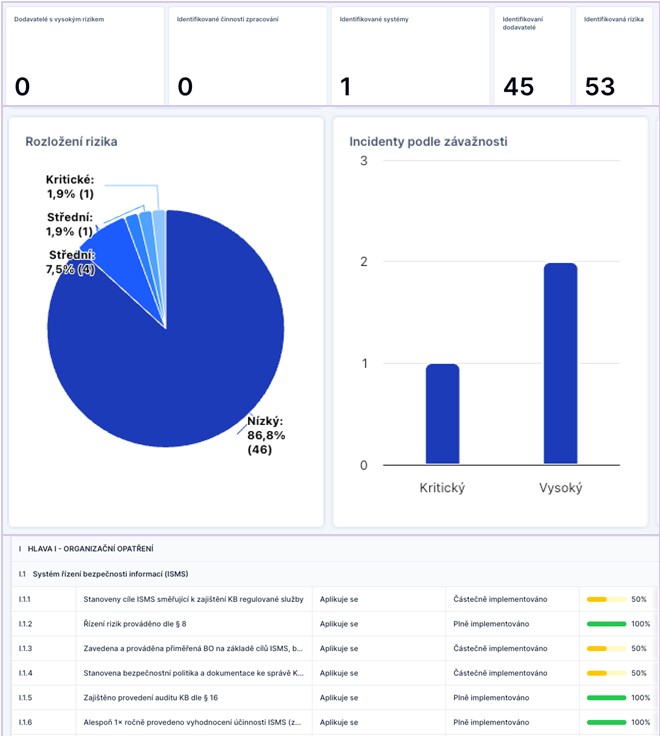
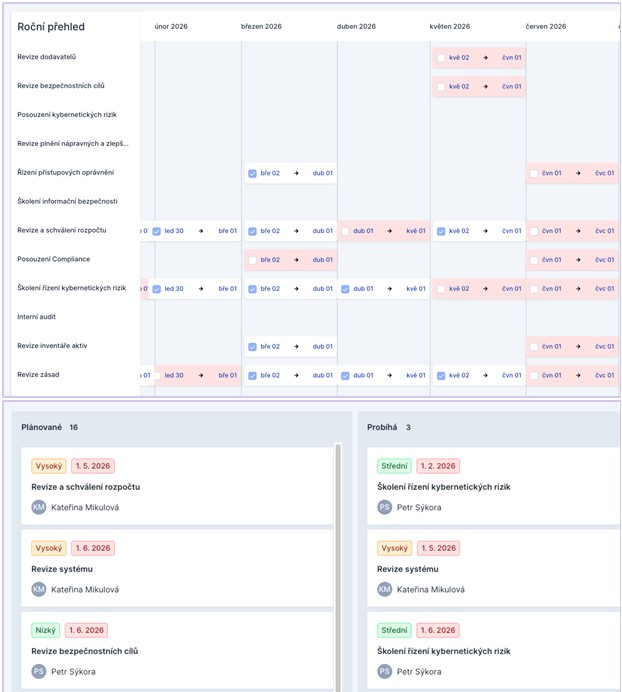
Software Support for the Service – a unified environment in which we manage risks, incidents, assets, vendors, documentation, and reporting.
Packages for DORA, NIS2 (ZKB), ISO 27001, GDPR, the AI Act, TISAX, and more.
Integrations with Jira, MS Teams, Slack, Entra ID, and more.
Support for collaboration and automation.
We’ll handle your cybersecurity management and compliance tasks for you — right within the cybreg platform, with an up-to-date overview for your management.
Governance, Compliance, and Reporting
We’ll take over security governance and communication with management—from consultations to regular reporting.
- Regular consultations with company management
- Establishment and Ongoing Review of Security Governance
- Review of the Allocation of Roles, Responsibilities, and Authorities
- Gap Analysis Against the Requirements of the CNB, NÚKIB, DORA, NIS2 (ZKB), ISO 27001, and CRA for Digital Product Manufacturers
- Roadmap for Corrective Actions and Setting Priorities
- Regular Reporting on Security Status to Management

Risk, Asset, and Supplier Management
We continuously manage security risks and oversee our suppliers—from methodologies to contractual requirements.
- Review of the Methodology for Managing ICT and Security Risks
- Review of Risk Register Management and Risk Profile Updates
- Assessment of New Technologies and Projects from a Risk Perspective
- Recommendations for Mitigation and Compensatory Measures
- Review of Critical ICT Suppliers and Contractual Security Requirements
- Support for Evaluating Cloud and SaaS Services
Incidents, Business Continuity, and Audit Support
We’ll prepare you for incidents, outages, and audits—and we maintain complete security documentation.
- Review of the incident and vulnerability management process, support in resolving incidents, and compliance with reporting requirements
- Review of BCP/DR Documentation and Evaluation of Continuity Tests
- Review and Update of Policies, Guidelines, Methodologies, and Registers
- Preparation for internal and external audits; support during inspections by the Czech National Bank (ČNB) and the National Cyber and Information Security Agency (NÚKIB)
- Proposing and Monitoring Corrective Actions Based on Audit Findings
Frequently Asked Questions
Everything You Need to Know About CISO as a Service.
Who is this service intended for?
For organizations that need to systematically manage cybersecurity but do not have their own experienced CISO or wish to strengthen their internal team. We primarily assist with ZKB/NIS2, DORA, ISO 27001, and CRA requirements.
What does CISO stand for, and what are the CISO's responsibilities?
CISO stands for Chief Information Security Officer. The CISO is responsible for managing cybersecurity, risks, incidents, vendors, security documentation, audits, and reporting to company management.
Does the external CISO role encompass that of a cybersecurity manager?
Yes. As part of the service, an external CISO can also serve as a cybersecurity manager under the ZKB. We always tailor the specific arrangements to the organization’s responsibilities and needs.
How does the service help with DORA, NIS2, and ZKB?
We will assess the current situation, develop a plan for corrective actions, and assist with its implementation. We address risks, assets, suppliers, incidents, business continuity, documentation, and preparation for inspections and audits.
Does an external CISO replace management's responsibility?
No. An external CISO takes over the technical and operational management of security, but ultimate responsibility remains with the company’s management. We provide them with regular updates on risks, incidents, and the implementation of security measures.
Would you like to learn more?
For more information about the CISO as a Service offering, please feel free to contact us at +420 608 031 240 or via the contact form.