Cybersecurity and Compliance Simply and Verifiably
Our platform and experts will help you manage the tasks associated with NIS2 (ZKB), DORA, ISO 27001, CRA, and other regulations.
- Smart IT solutions for risk management, cybersecurity, and compliance with DORA, NIS2 (ZKB), and other regulatory frameworks.
- As part of the CISO as a Service (Chief Information Security Officer), we’ll help you manage the tasks related to information and cybersecurity.
- We will guide you through the entire process—from a GAP analysis and the design of appropriate measures, through their implementation and ongoing support, to preparation for audits and regulatory inspections.
- FINREG PARTNERS' attorneys will ensure that the documentation complies with the current regulations.
Effective digitalisation of compliance and risk management
Smart IT solutions for risk management and compliance with DORA, NIS2 but also with other regulatory frameworks. Pre-prepared data and a comprehensive implementation process in accordance with regulatory requirements.
CISO as a Service
CISO as a Service provides you with an experienced external expert and a team of specialists who will take over the systematic management of your organization’s cybersecurity, risks, and regulatory obligations.
The cybreg platform
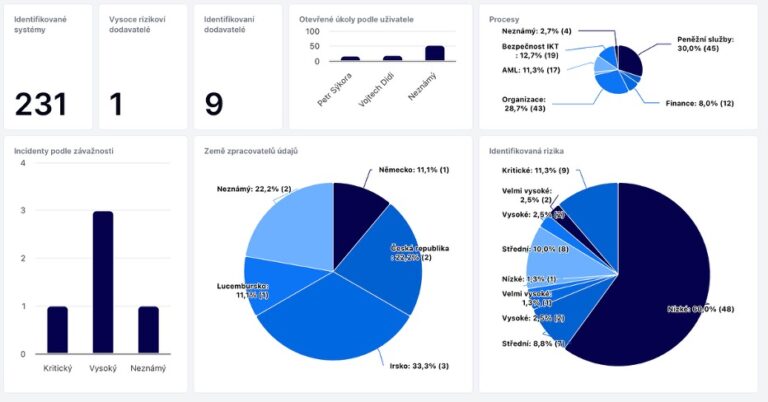
The platform integrates compliance, risk management, and cybersecurity into a single environment. It enables you to manage regulations, assets, risks, suppliers, incidents, documentation, and related tasks in a clear and efficient manner.
cybreg.dora
Compliance with DORA
cybreg will make it easier for you to manage ICT risks and ensure DORA compliance. It offers management of internal regulations, incidents, risks and suppliers with automation and integration with tools such as Jira, Asana, MS Teams.
cybreg.nis2
Compliance with NIS2 (ZKB)
The cybreg software enables you to meet the requirements of the Cybersecurity Act and ensure compliance with NIS2 through process automation and effective risk management.
Cybersecurity Training
Hands-on training focused on ZKB requirements and cybersecurity for management, administrators, and regular users. We help organizations strengthen security awareness, manage risks effectively, and prepare employees for current cyber threats and regulatory requirements.

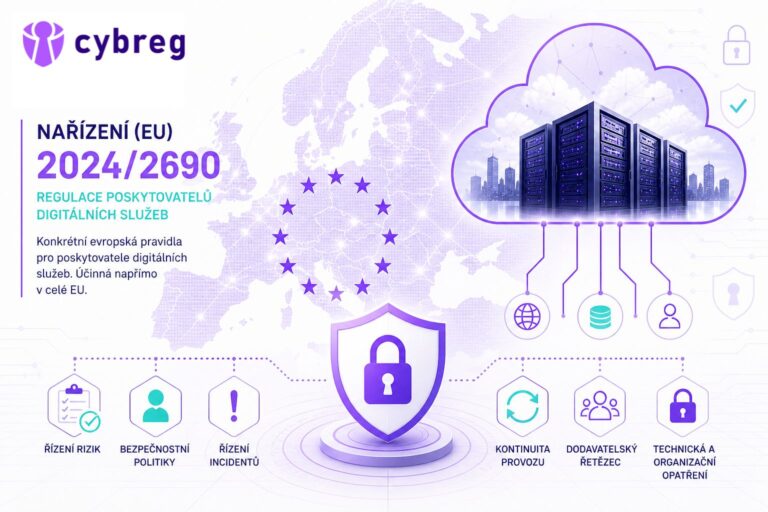
Digital services under EU scrutiny
Digital Services Regulation: a regulation that is often forgotten Recently, there has been virtually no talk of anything other than the NIS2 directive and the new law on cyber security. Companies are intensively discussing whether they will fall under the new regulation, under what regime and what obligations will arise for
Why Excel is not enough: DORA requires real software
The Digital Operational Resilience Act (DORA) is fundamentally changing the approach to ICT risk management and cyber security. Whereas previously a combination of documents, spreadsheets and one-off audits could suffice, today a continuous, managed and demonstrable system is expected. It is in this context that Excel, as widespread and practical as

New Cybersecurity Act Underway. What are the First Steps of Newly Regulated Organizations?
On November 1, 2025, the long-awaited Cybersecurity Act will come into effect, bringing changes to the Czech legal system based on the European NIS2 Directive. This is a fundamental change that expands the circle of regulated entities from several hundred to several thousand across the Czech Republic, ranging from energy and
Frequently Asked Questions
Everything you need to know about cybreg compliance and risk management software.
What is cybreg, and how can it help you?
Cybreg combines a software platform for managing cybersecurity and compliance with the expert services of an external CISO. It helps you manage risks, incidents, assets, vendors, documentation, tasks, and reporting to senior management—all in one place.
What regulations and standards will the CISO as a Service help us comply with?
Our services focus primarily on the new Cybersecurity Act, NIS2, DORA, ISO 27001, and preparing digital product manufacturers for the requirements of the Cyber Resilience Act. We can assist you with GAP analysis, the design and implementation of measures, risk management, documentation, reporting, and preparation for audits and inspections by the Czech National Bank (ČNB) or the National Cyber Security Agency (NÚKIB).
Do we need to have our own CISO or security team?
No. An experienced external CISO with a team of specialists can take on an agreed-upon scope of work or supplement your existing team. For organizations subject to the Cybersecurity Act, an external CISO can also serve as the cybersecurity manager.
How does the collaboration with cybreg work?
We begin by assessing the current state and conducting a gap analysis. We then prepare a roadmap and set priorities, assist with the implementation of measures, and provide ongoing support through regulatory audits and inspections. We track individual tasks, risks, measures, and evidence directly within the cybreg platform.
The cybreg platform supports requirements management in accordance with DORA, NIS2, the Czech Cybersecurity Act, ISO 27001, the GDPR, the Cyber Resilience Act, the AI Act, TISAX, and others. The platform is continuously being expanded to support additional regulatory frameworks, standards, and related requirements.