
Cybersecurity Act / NIS2
The cybreg software enables you to ensure compliance with the NIS2 directive and meet the legislative obligations under the new Cyber Security Act (CSA).
- Internal regulations, incident management, risk management, roles and responsibilities.
- Automation of cybersecurity processes within supply chains.
- Our experts will guide you through the GAP analysis and the entire implementation process.
- The legal team at FINREG PARTNERS will ensure compliance in your internal regulations and security policies

The NIS2 Directive establishes a European framework for enhancing cybersecurity in selected sectors.In the Czech Republic, its requirements have been transposed into the new Cybersecurity Act and related regulations. In practice, this means that by complying with the obligations set forth in the new Cybersecurity Act, Czech organizations also meet the requirements stemming from the NIS2 Directive.
The regulations emphasize not only technical measures but also systematic risk management, management accountability, supply chain security, incident response, and evidence-based management of the entire field of cybersecurity.
- cybersecurity risk management,
- recording and evaluation of assets,
- security incident management,
- supplier security,
- safety measures and documentation,
- governance and management accountability.
ZKB / NIS2 applies to a wide range of entities, from the energy and healthcare sectors to digital services and manufacturing.
Energy
Production, distribution, and other regulated services in the energy sector.
Digital Infrastructure and ICT
Providers of electronic communications, data centers, cloud services, and other digital services.
Health Care
Hospitals, healthcare providers, and other relevant entities.
Transportation
Selected organizations operating in road, rail, air, or water transportation.
Public Administration
Selected public sector agencies and organizations.
Manufacturing and Other Sectors
The regulations also affect certain manufacturing companies, logistics, waste management, the food industry, and other sectors.
Not sure if the new cybersecurity law applies to you?
ZKB / NIS2 Implementation
Under ZKB / NIS2 and related cybersecurity regulations, it is necessary to systematically implement security measures, responsibilities, processes, and related documentation into the organization’s operations. The implementation process also includes assessing the current status, identifying gaps, and establishing specific steps to achieve compliance with regulatory requirements.
The cybreg platform includes a guide that walks you through the entire process of implementing ZKB/NIS2 requirements. With cybreg, you gain a key tool for compliance with the Cybersecurity Act/NIS2. Our cybersecurity experts will advise you on GAP analysis and the entire implementation process. The legal team at FINREG PARTNERS will ensure that your internal regulations and security policies comply with applicable regulations.
Identification and valuation of assets
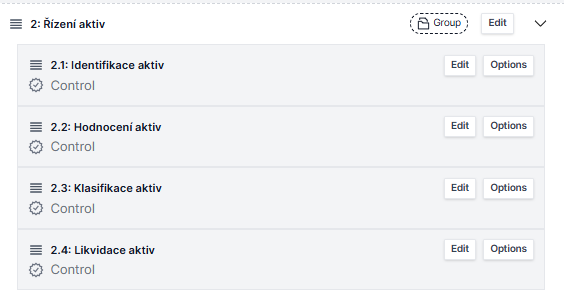
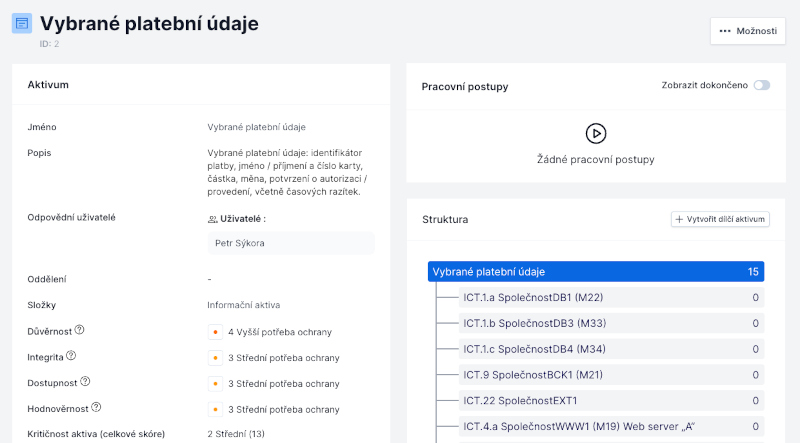
Under the ZKB / NIS2 and related cybersecurity regulations, it is necessary to identify and record relevant assets, determine their significance, owners, and interrelationships, and assess their importance from the perspective of the organization’s security and operations.
The cybreg software includes a registry of the company’s assets, their interconnections and dependencies, including the responsible persons and other attributes. Identifying and assessing assets from a cybersecurity perspective is one of the fundamental steps in implementing measures based on the Cybersecurity Act.
Risk Management
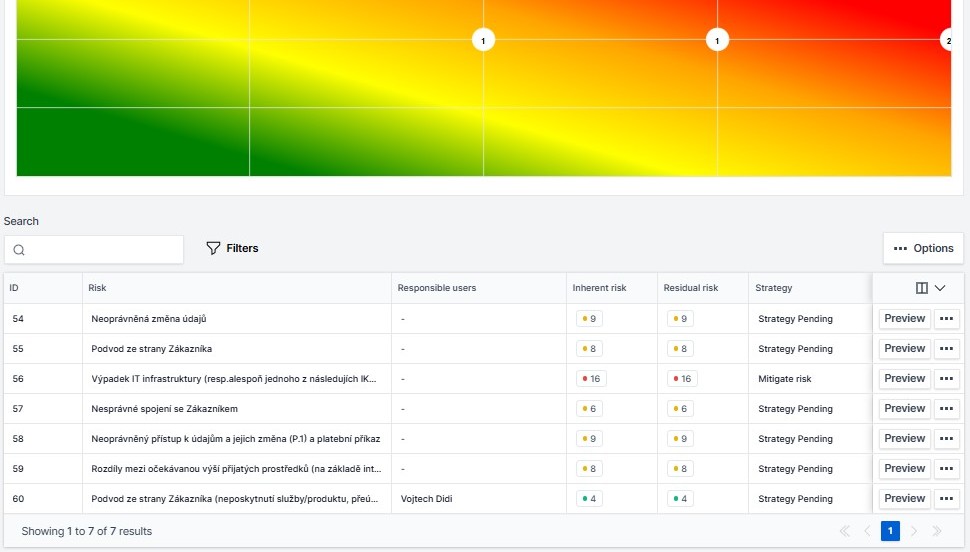
Under the ZKB/NIS2 and related cybersecurity regulations, it is necessary to continuously identify, assess, and manage risks related to information assets, processes, and the services provided. An organization must be able to determine the level of risk, select an appropriate strategy for managing it, and provide verifiable evidence of the measures taken.
The Cybreg software ensures the management and maintenance of a risk catalog in accordance with ZKB/NIS2 requirements, including risk mapping and the calculation of the resulting risk level. For each risk, a strategy (risk acceptance or risk mitigation) can be selected, along with all supplementary information. Cybreg documents everything and enables you to demonstrate proactive risk management. The software includes a comprehensive overview of the organization’s risks, including asset valuation and interconnections with other compliance elements.
Statement of Applicability under ZKB / NIS2
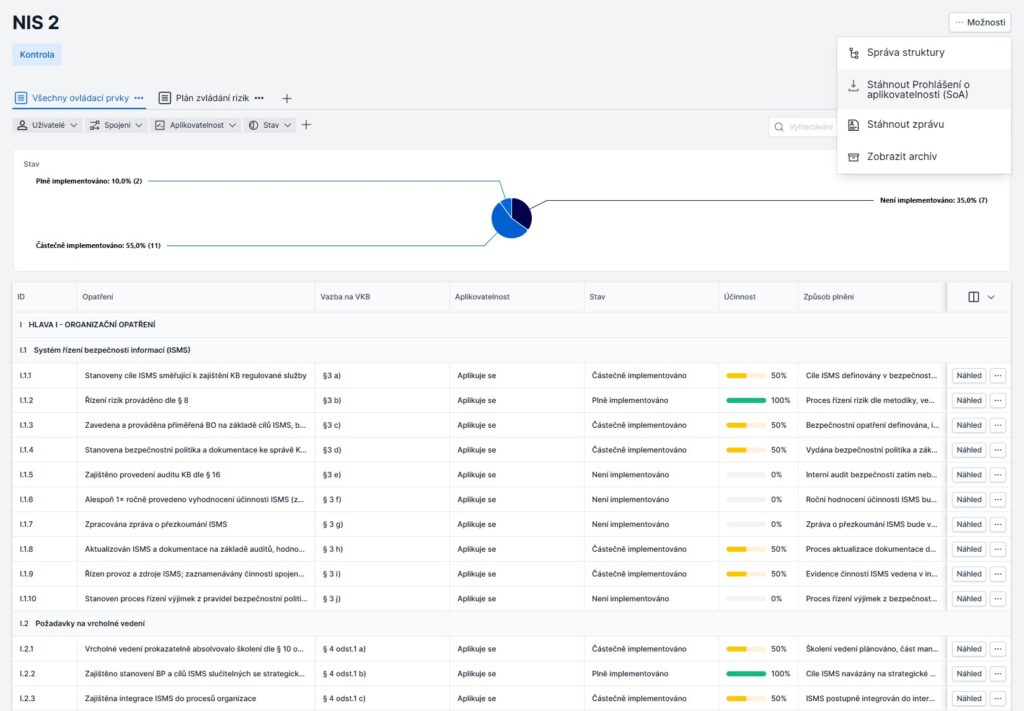
As part of the ZKB/NIS2 requirements, it is necessary to identify which security measures have been implemented within the organization and, where applicable, why certain measures have not been implemented and what prevents their implementation. The Statement of Applicability is a key document that specifies which security measures are relevant and how they are being implemented.
By integrating asset tracking, risk management, and a catalog of measures, cybreg makes it easy to create this document, update it on an ongoing basis, and maintain it in an auditable format without unnecessary manual work.
Incident Management
Under the ZKB / NIS2 and related cybersecurity regulations, it is necessary to ensure the systematic detection, recording, assessment, and resolution of cybersecurity events and incidents. The process also includes properly defining responsibilities, monitoring the course of an incident, and complying with any applicable notification and reporting requirements.
The cybreg platform enables you to respond to security incidents in a timely and appropriate manner in accordance with established plans. It helps you monitor deadlines for mandatory incident reporting and document and demonstrate the work performed in response to security incidents.

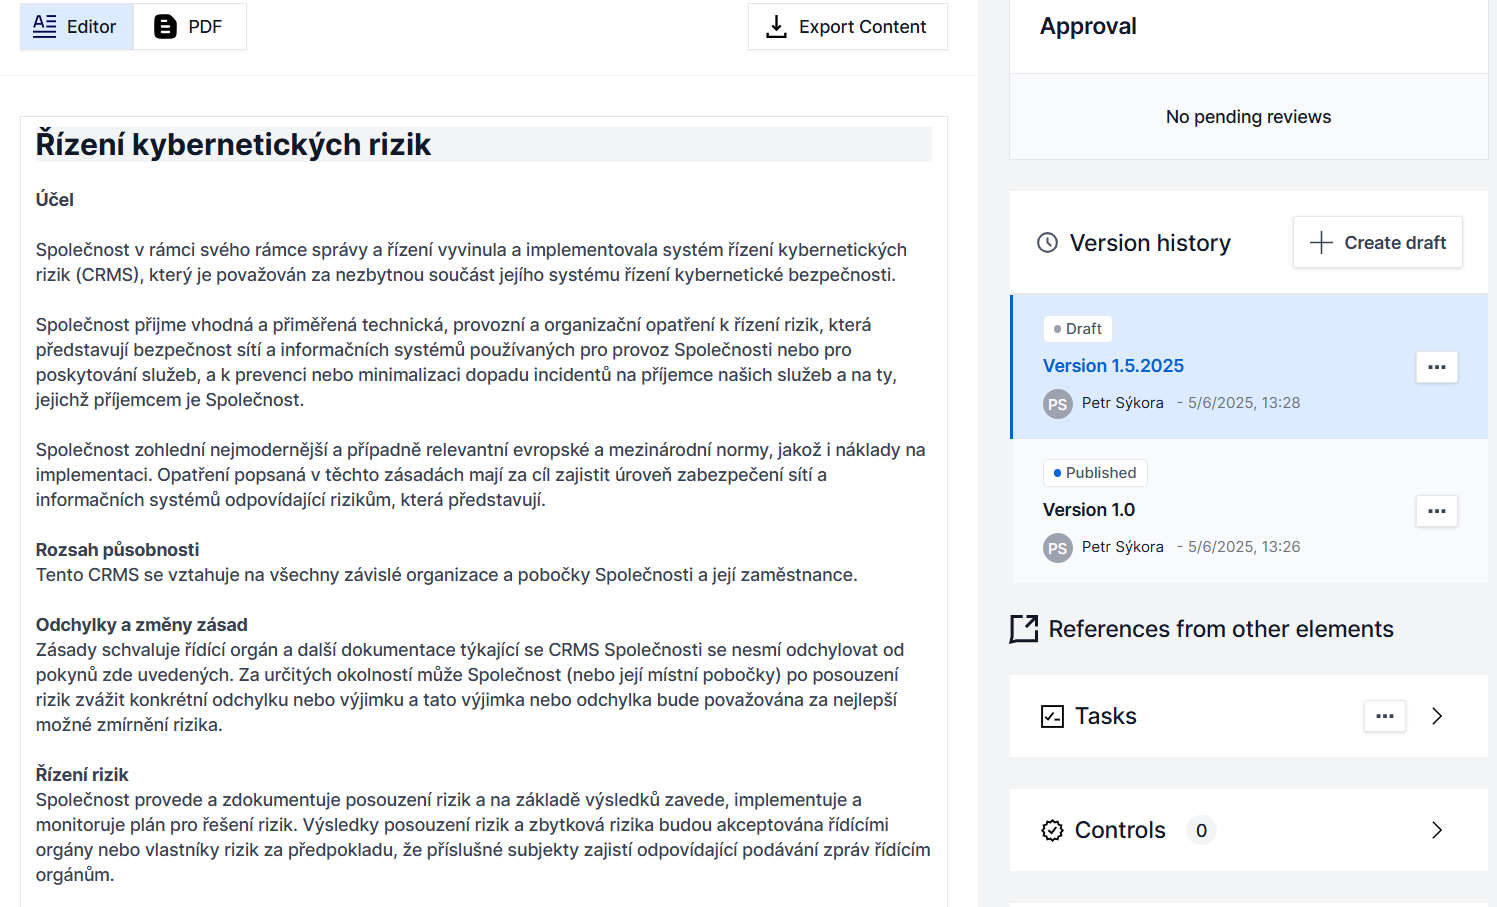
Managing security policies
ZKB / NIS2 requires organizations to establish and maintain appropriate security policies, internal regulations, and other documentation. These documents must reflect the actual processes, responsibilities, assets, and security measures in place and must be updated regularly.
The cybreg platform supports the centralized management of security documentation, including version control, approval, and integration with other elements of cybersecurity management. Documents can be linked, for example, to assets, risks, measures, and responsible parties, while also tracking changes and approval history.
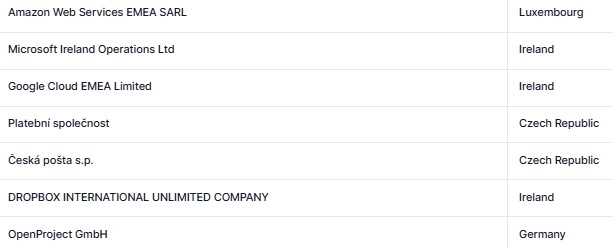
Supplier Evaluations and Audits
Supply chain security management is one of the key areas of ZKB / NIS2. Organizations must therefore take into account the cybersecurity risks associated with their suppliers and service providers and continuously verify that they meet the established security requirements.
The software allows you to automate and streamline mandatory supplier audits and comply with the relevant requirements under ZKB / NIS2. Integration with tasks and the ability to automatically distribute questionnaires within the cybreg platform.
Customization, Automation and Integration
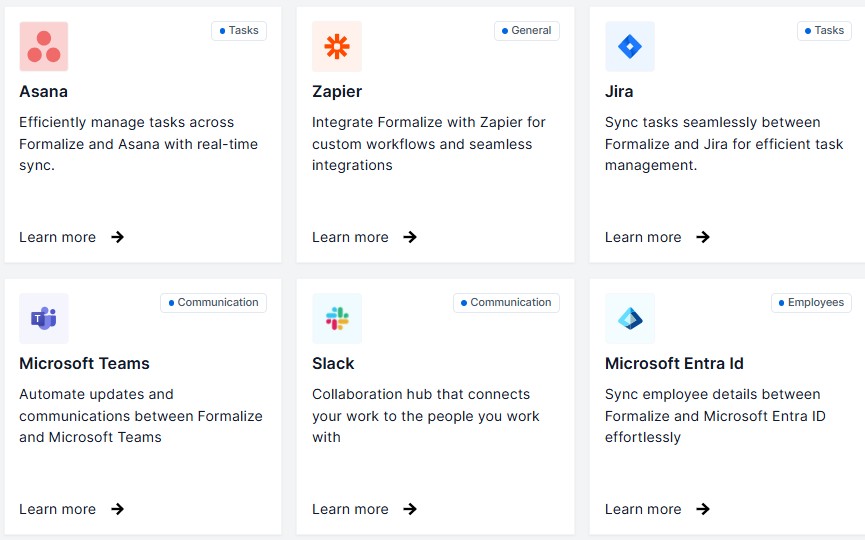
Effective cybersecurity management requires collaboration among multiple teams, regular task completion, and the handling of information across various systems. Automation and the integration of the tools used therefore help reduce manual tasks and simplify day-to-day compliance management.
We can customize the cybreg software according to your needs. The basis of the range of functionalities is the wide possibility of automating individual processes and the associated savings in cybersecurity compliance costs. Of course, it is possible to integrate with other tools used within the organization such as Jira, Asana, MS Teams, Slack, Service Now and others.
Cybersecurity management is not the responsibility of a single person.
Regulation requires a clear division of authority and responsibility between the organization’s leadership and professional roles.
Senior Management
It approves the overall direction of cybersecurity, makes key decisions, and oversees risk management.
Cybersecurity Manager
Coordinates the cybersecurity management system, risks, security measures, and related processes.
Cybersecurity Architect
It designs a security architecture and helps ensure that appropriate technical and organizational measures are in place.
Cybersecurity Steering Committee
It supports the coordination of cybersecurity across the organization and oversight of key decisions.
Asset Guarantor
It describes a specific asset, its significance, and the requirements for its protection.
Cybersecurity Auditor
It independently verifies the functioning of the management system and the security measures in place.
Individual roles need to work with shared information, but each has different responsibilities and tasks.
The cybreg platform links assets, risks, measures, incidents, documentation, and responsibilities so that executives, cybersecurity managers, asset owners, and other roles can all work with the same up-to-date data.
Don't you have all the necessary roles in-house?
As part of CISO as a Service , an external expert and a team of specialists can take over the systematic management of cybersecurity, risks, suppliers, incidents, and regulatory obligations. Cybreg currently markets this service specifically as support for ZKB/NIS2, DORA, ISO 27001, and other frameworks; an external CISO can also serve as the cybersecurity manager in accordance with ZKB/NIS2.
The cybreg platform links regulatory requirements to your organization’s actual processes.
Link regulatory requirements to assets, risks, security measures, incidents, suppliers, documentation, and responsibilities.
Schedule a demo of the cybreg platform
Frequently Asked Questions
Everything You Need to Know About the NIS2 Directive in the cybreg Environment.
What is the NIS2 Directive?
NIS2 (Network and Information Security Directive 2) is a European directive on the security of networks and information systems. In the Czech Republic, it has been transposed by the new Cyber Security Act (ZKB), effective from 1 November 2025, which expands the range of regulated entities from several hundred to thousands of organisations.
Who is affected by ZKB / NIS2?
ZKB/NIS2 applies to medium and large enterprises in critical sectors—energy, transportation, banking, healthcare, and public administration. In the Czech Republic, specific obligations are defined by ZKB, and oversight is provided by NÚKIB.
What is the difference between NIS2 and ZKB?
NIS2 is a European directive, the ZKB is its Czech transposition – the Act on Cyber Security effective from 1 November 2025.The ZKB specifies the requirements of NIS2 for the Czech environment and adds specific obligations to the NUCIB, including the mandatory registration of a regulated service within 60 days.
What are the consequences of non-compliance with ZKB / NIS2?
Failure to comply with the obligations under ZKB / NIS2 may result in administrative sanctions and fines of up to 10 million EUR or 2% of global annual turnover for core entities. The organization’s management is also responsible for cybersecurity.
How to Implement ZKB/NIS2 Compliance in Your Company?
Cybreg offers a guide to the entire NIS2 implementation process – from GAP analysis to risk catalog management and security policy management to automated vendor audits. FINREG PARTNERS’ legal team ensures compliance of internal regulations with applicable legislation.
How does NIS2 relate to DORA?
NIS2 and DORA are complementary regulations. ZKB/NIS2 applies to a broader range of entities across various sectors, while DORA is specific to the financial sector, with an emphasis on digital resilience and ICT risks. Cybreg software addresses both regulations in a single system.
What role does NÚKIB play in the implementation of ZKB / NIS2?
NÚKIB (National Cyber and Information Security Agency) is the key regulator overseeing compliance with the ZKB / NIS2. Organizations must report a regulated service within 60 days and, following registration, meet other statutory deadlines.