
Digital Operational Resilience Act (DORA)
Through the cybreg platform, you can easily implement ICT risk management and meet the requirements of the DORA regulation.
- Internal regulations, incident management, risk catalogue, roles and responsibilities
-
Information register, management of information, ICT and support assets
- Generation of mandatory reports in accordance with CNB requirements

DORA – the Digital Operational Resilience Act – is a European regulation focused on the digital operational resilience of the financial sector. Its goal is to ensure that financial institutions are able to prevent problems related to information and communication technologies, manage cyber incidents and outages, and restore their operations without a significant impact on the financial services they provide.
DORA takes effect on January 17, 2025, and establishes a unified framework for ICT risk management across the financial sector.
The regulation harmonizes requirements, particularly in the following areas:
- ICT risk management,
- incident tracking and reporting,
- digital operational resilience testing,
- third-party risk management,
- management of contracts with ICT service providers,
- governance and management accountability.
DORA affects a wide range of entities operating in the financial sector.
Payment Institution
DORA’s scope of application covers payment institutions and other providers of regulated payment services.
Banks and Credit Institutions
The DORA requirements apply, for example, to banks and other credit institutions.
FinTech companies
DORA may apply to companies that provide regulated financial services through technology solutions.
Investment Companies
The regulations apply, for example, to securities dealers, investment firms, and other capital market entities.
Cryptocurrency Exchanges
DORA’s scope of authority also includes selected providers of cryptoasset services.
ICT Service Providers
DORA also significantly regulates the relationships between financial institutions and their ICT service providers.
Not sure if DORA applies to you?
DORA implementation
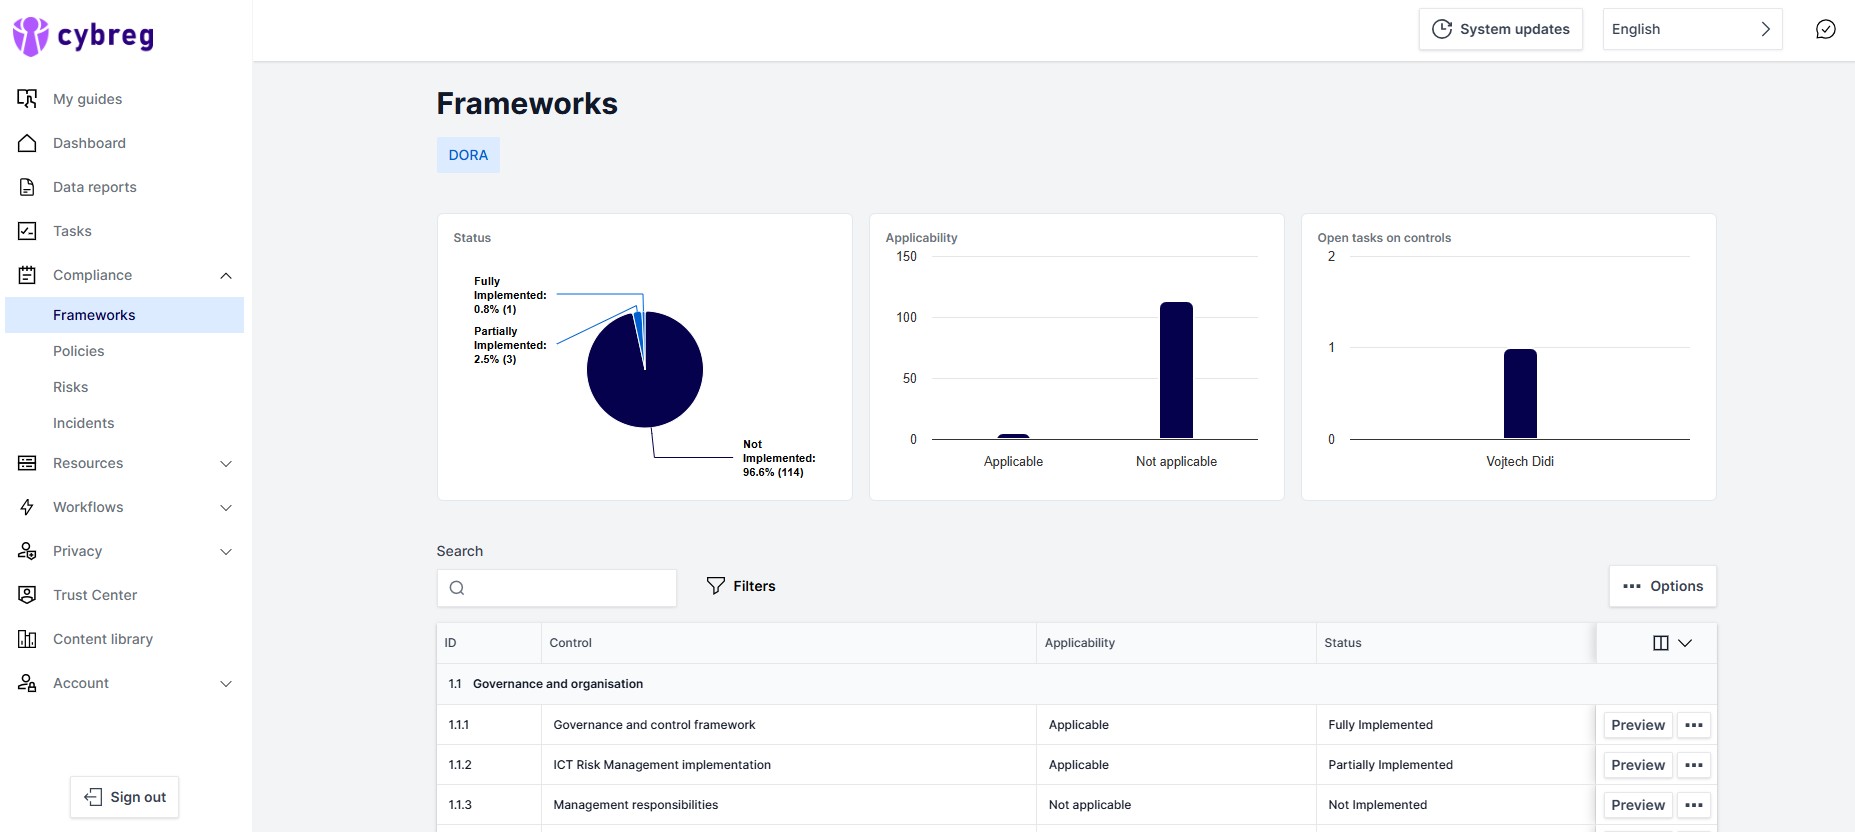
Under DORA, it is necessary to ensure the systematic implementation of regulatory requirements into the organization’s internal processes, documentation, responsibilities, and related assets. Individual requirements must be correctly identified, their relevance assessed, and their compliance continuously monitored.
The cybreg software includes a wizard that guides you through the entire process of ensuring compliance with DORA requirements. Specialized legal and regulatory experts will help you create customized internal policies and processes, including links to information assets, ICT assets, specific activities, and other functionalities. With cybreg, you’ll gain key data and a comprehensive framework for ensuring DORA compliance.
Management of Information and ICT Assets
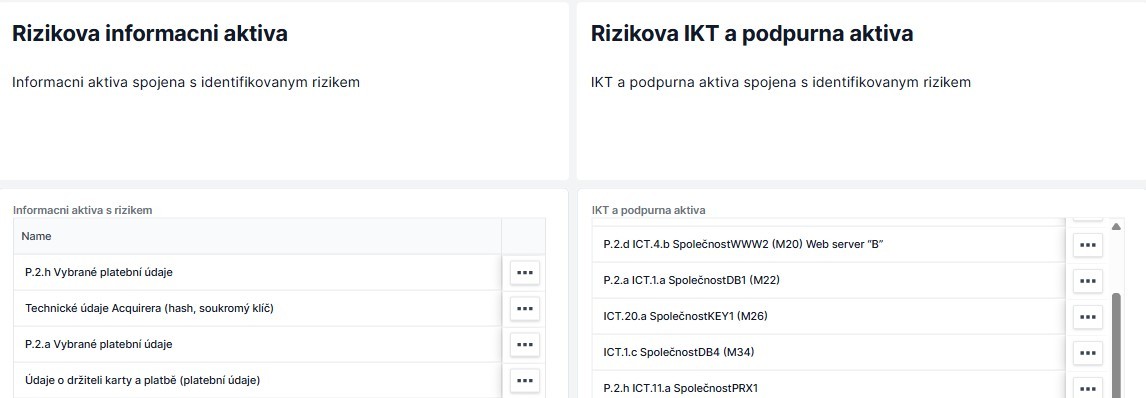
DORA requires financial institutions to maintain an overview of the information and ICT assets that support their operations and to be able to identify their significance, owners, interdependencies, and associated risks.
The cybreg platform includes a catalog of all information assets and ICT assets. It allows you to store and view information about assets and the individuals responsible for managing each asset. With the cybreg software, you can identify all processes related to information and ICT assets, as well as monitor the physical or digital security of these assets.
ICT risk management
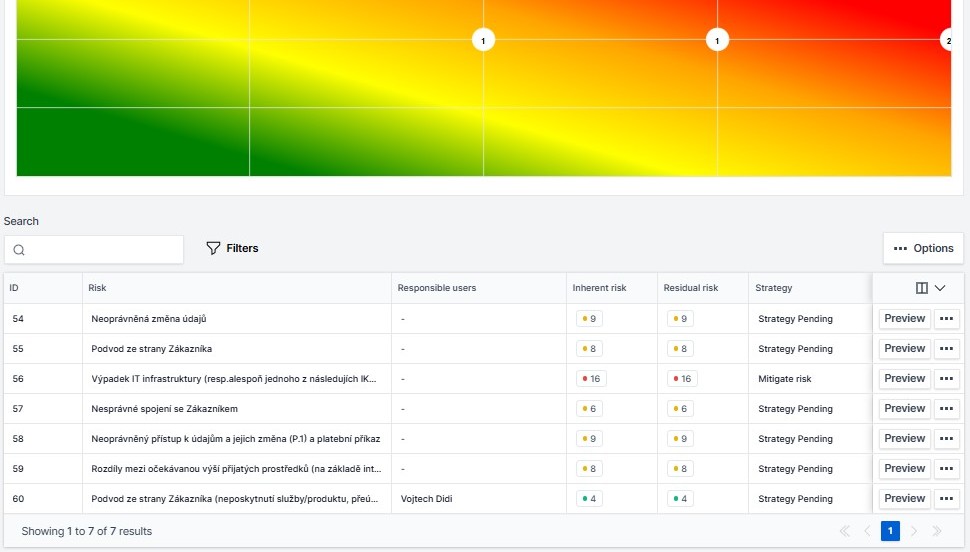
Under DORA, organizations must continuously identify, assess, and manage ICT risks, including their likelihood, impact, and the measures taken. At the same time, risk management must be integrated with assets, processes, and other relevant areas.
The cybreg platform ensures the management and maintenance of a risk catalog in accordance with DORA, including risk mapping and the calculation of overall risk levels based on probability and impact. The software includes a diagram that provides a comprehensive and clear overview of risks. The software also enables comprehensive integration with other elements, such as your business activities, information assets, and ICT assets, and supports the requirements of the NIS2 Directive and cybersecurity standards.
Managing risks associated with third parties
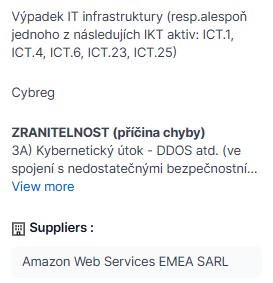
Under DORA, it is necessary to manage the risks associated with the use of third-party ICT service providers. Organizations must maintain an overview of their suppliers, the associated risks, and contractual relationships, and ensure that contracts include the required regulatory provisions.
As part of ICT risk management, the cybreg software enables the management and control of risks associated with third-party ICT service providers. This primarily involves the regulatory management of contracts entered into with third-party ICT service providers and ensuring that the content of such contracts complies with DORA. The software also enables the automation of the process of monitoring and auditing the activities of third-party ICT service providers, as required by the DORA Regulation for such monitoring or auditing. Cybreg also offers a CISO-as-a-Service solution through outsourcing.
Questionnaires for selecting third-party ICT service providers
Under DORA, when selecting and evaluating ICT service providers, it is necessary to consider their ability to meet the organization’s security, operational, and regulatory requirements. The evaluation of a supplier should therefore be based on uniform and verifiably documented criteria.
The cybreg platform will generate questionnaires for you to send to candidates for third-party ICT service providers. The questionnaires contain all the necessary information you will need to evaluate when selecting third-party ICT service providers and ensure that all relevant questions are covered so that a candidate can be selected in accordance with DORA requirements.
Register of information
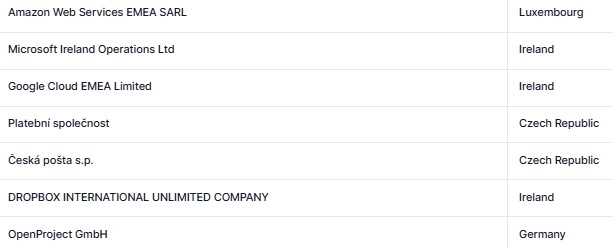
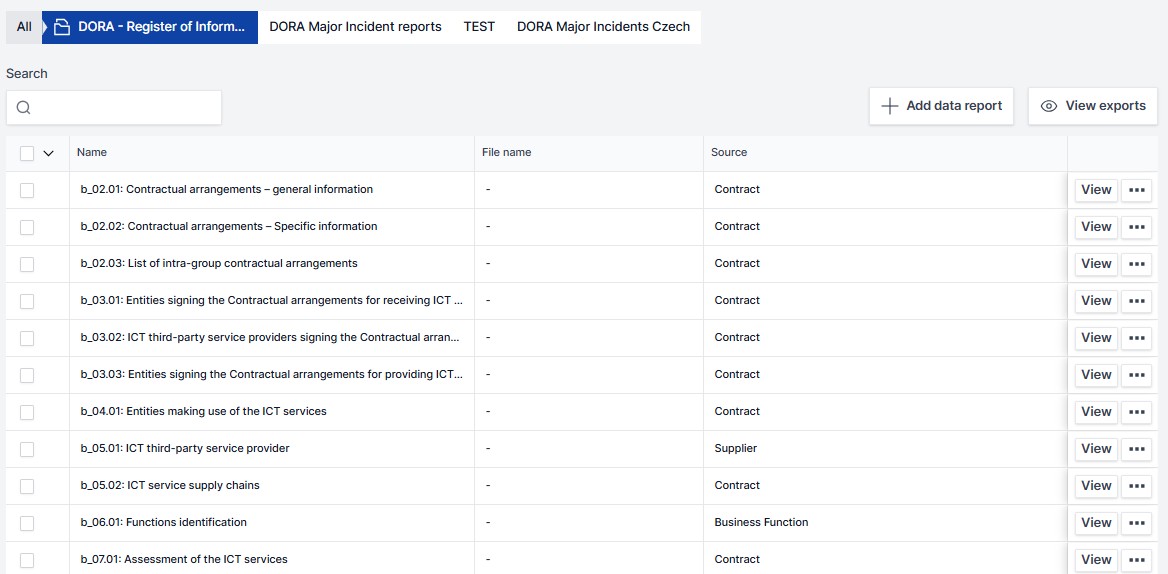
DORA requires financial institutions to maintain and continuously update a registry containing information on contractual arrangements with third-party ICT service providers. The register must contain specified information about suppliers, services provided, contractual relationships, and other relevant connections.
The cybreg software comprehensively and clearly manages the record of information about third-party ICT service providers and the services they supply to you in the information register. The information register follows the format and scope prescribed for such a register under DORA. The cybreg software manages the information register so that it can be conveniently submitted to the CNB with all the necessary information at any time upon request.
Incident Management
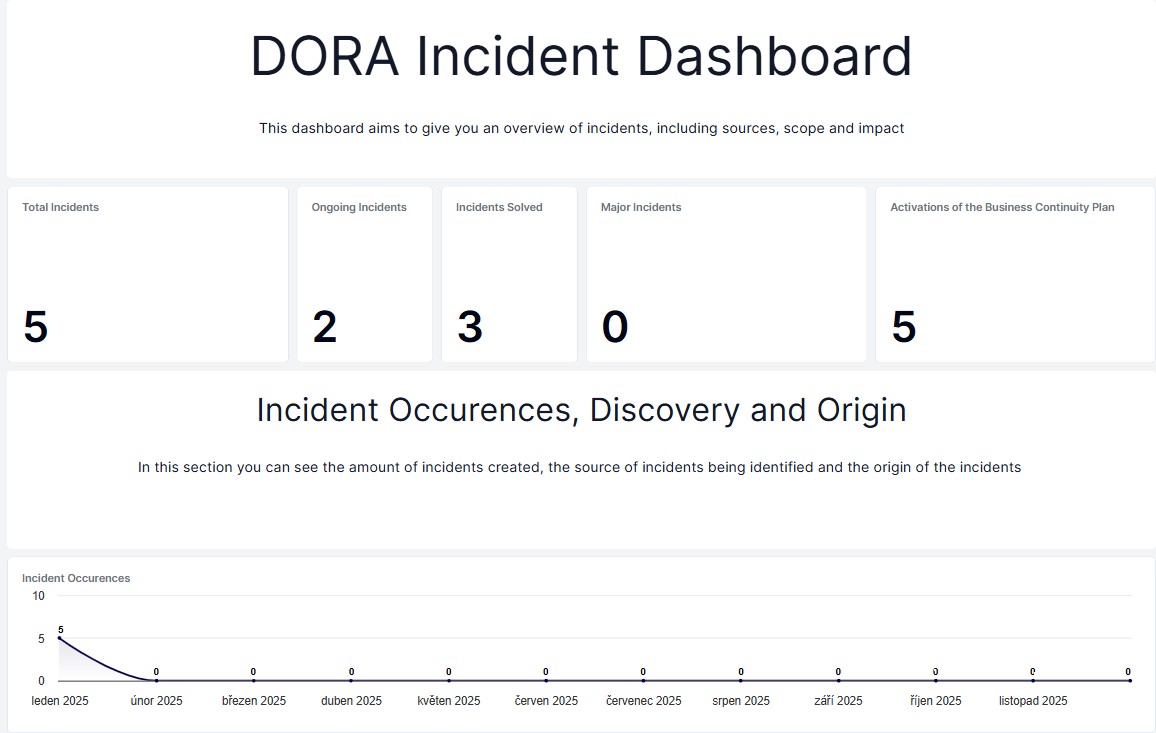
Under DORA, it is necessary to ensure the systematic recording, classification, management, and evaluation of ICT-related incidents. The organization must be able to track their progression, impacts, causes, and links to the affected assets, processes, and services.
The cybreg software manages and generates the necessary documentation for incident management, should incidents occur, in accordance with DORA requirements. Incident management includes detailed integration with information assets, ICT assets, processes, risks, and other elements. Individual steps can be automated. When an incident occurs, the software ensures that the relevant reports are generated for submission to the Czech National Bank (ČNB).
Reporting in DORA Mode for the CNB
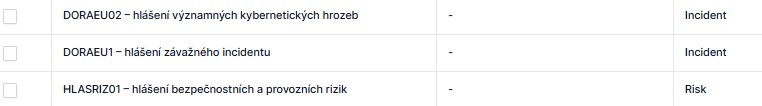
DORA establishes the obligation to classify serious ICT-related incidents and, where applicable, to report them to the CNB within the specified timeframes and in the required format.
The cybreg software makes it easy to generate all reports submitted to the CNB under the DORA system, ensuring they meet the required content standards so that they can be submitted in the format required by the CNB.
Periodic reports
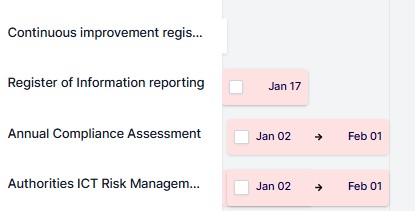
In addition to incident management, DORA also requires compliance with other regular regulatory and record-keeping obligations. Organizations must therefore keep track of deadlines, responsibilities, and the documentation required for individual reports and other recurring tasks.
The cybreg platform manages and generates the necessary documentation for incident management, should incidents occur, in accordance with DORA requirements. Incident management includes detailed integration with information assets, ICT assets, processes, risks, and other elements. Individual steps can be automated. When an incident occurs, the software ensures that the appropriate reports are generated for submission to the Czech National Bank (ČNB).
Flexibility, automation and integration
Compliance with DORA requirements affects a wide range of processes and teams across the organization. For effective compliance management, it is therefore important that individual activities, tasks, and information not be isolated in separate systems and that selected steps can be automated.
We can customize the cybreg platform to meet your specific needs. At the heart of many of its features is the extensive ability to automate individual processes and the resulting cost savings associated with ensuring compliance with DORA. Of course, it can be integrated with other tools used within your organization, such as Jira, Asana, MS Teams, Slack, ServiceNow, and more.
DORA places great emphasis on clearly defined competencies, responsibilities, and oversight of ICT risk management. This goes beyond mere technical IT roles. The organization’s leadership, security specialists, risk management, compliance, internal audit, and operations teams are all involved in ensuring compliance.
Management / Governing Body
He is responsible for the ICT risk management framework, its approval, and regular oversight of its operation.
CISO
He coordinates cybersecurity, risk management, security measures, incidents, and related processes.
Risk Manager
It ensures the identification, assessment, and ongoing management of ICT risks and their integration with other business risks.
Compliance Officer
Monitors regulatory requirements, their implementation, and ongoing compliance within the organization.
Internal audit
It independently verifies whether the established processes, controls, and measures meet the requirements and are actually effective.
IT and Operations Teams
They implement technical measures, resolve incidents, manage systems, handle changes, perform backups, and ensure business continuity.
Collaboration among different roles is more effective when they work with the same data and processes in a single environment. The cybreg platform allows you to link risks, incidents, assets, suppliers, tasks, and responsibilities so that each role has access to the information it needs to do its job.
The cybreg team will help you achieve effective collaboration between roles and platforms, enabling you to outsource within the framework of CISO as a Service.
The cybreg platform links regulatory requirements to your organization’s actual processes.
From ICT risk and asset management to suppliers and incidents, to documentation, tasks, and regulatory reporting.
Schedule a demo of the cybreg platform
Frequently Asked Questions
Everything You Need to Know About DORA Compliance in the Cybreg Environment.
What is DORA?
DORA (Digital Operational Resilience Act) is a European regulation aimed at digital resilience in the financial sector. It sets out requirements for ICT risk management, incident management, digital resilience testing and third party risk management. It applies from 17 January 2025.
Who is covered by DORA?
DORA applies to financial entities – banks, insurance companies, investment firms, payment institutions, crypto-asset providers and key ICT service providers operating in the EU financial sector.
How to create a DORA information register?
The cybreg software includes a catalogue of all information assets, ICT assets and support assets. It allows you to store information about assets and responsible persons, identify established processes and monitor physical and digital security – all in accordance with DORA requirements.
How to report cyber incidents to the CNB under DORA?
The cybreg software enables the generation of mandatory reports in accordance with CNB requirements. It includes documentation and classification of incidents, management of cyber events and automation of the reporting process with links to relevant assets and processes.
How to manage third party risks under DORA?
Cybreg enables the management of contracts with third-party ICT providers, including their content according to DORA, automation of audits and questionnaires for the selection of providers. It provides regulatory oversight of contractual relationships.