
Link regulatory requirements to assets, risks, suppliers, policies, incidents, tasks, and evidence in a single environment. The Formalize platform helps you implement and continuously manage DORA, NIS2 (ZKB), ISO 27001, and other regulatory and internal frameworks—with clear responsibilities, automated workflows, and up-to-date reporting.

The Formalize platform integrates the various components of compliance and cybersecurity management systems. You can link a regulatory requirement to a specific control measure, risk, asset, supplier, responsible person, task, and evidence of compliance.
This gives the organization’s management an up-to-date overview of the compliance status, allows those responsible to clearly see their tasks, and enables the auditor to trace back decisions, approvals, changes, and related documentation.
The integration of risks, assets, systems, suppliers, measures, tasks, incidents, and evidence aligns with the platform’s current architecture and its multi-framework management approach.

The Formalize platform is based on software from a Danish company Formalize, which develops risk management and compliance solutions for organizations across countries and industries. We combine its technological infrastructure with the cybreg team’s expertise in cybersecurity, regulation, and the Czech market.
Formalize: the software foundation
Provides a software environment that integrates requirements, actions, risks, documentation, and tasks into a single system.
cybreg: specialized content for the Czech market
We develop and maintain Czech-language packages that translate regulatory requirements into a framework of measures, sample documentation, and work procedures. This provides you with a foundation for implementing these requirements in practice, which you can adapt to the needs of your organization.
Formalize offers pre-built integrations as well as a public API for custom integrations. This allows you to integrate the platform into your existing environment and reduce the need for manual data transfer between systems.
Ready-made integrations include Jira, Microsoft 365, Asana, Monday.com, and ClickUp. You can work with the cybreg team to assess integration options based on your organization’s systems and processes.
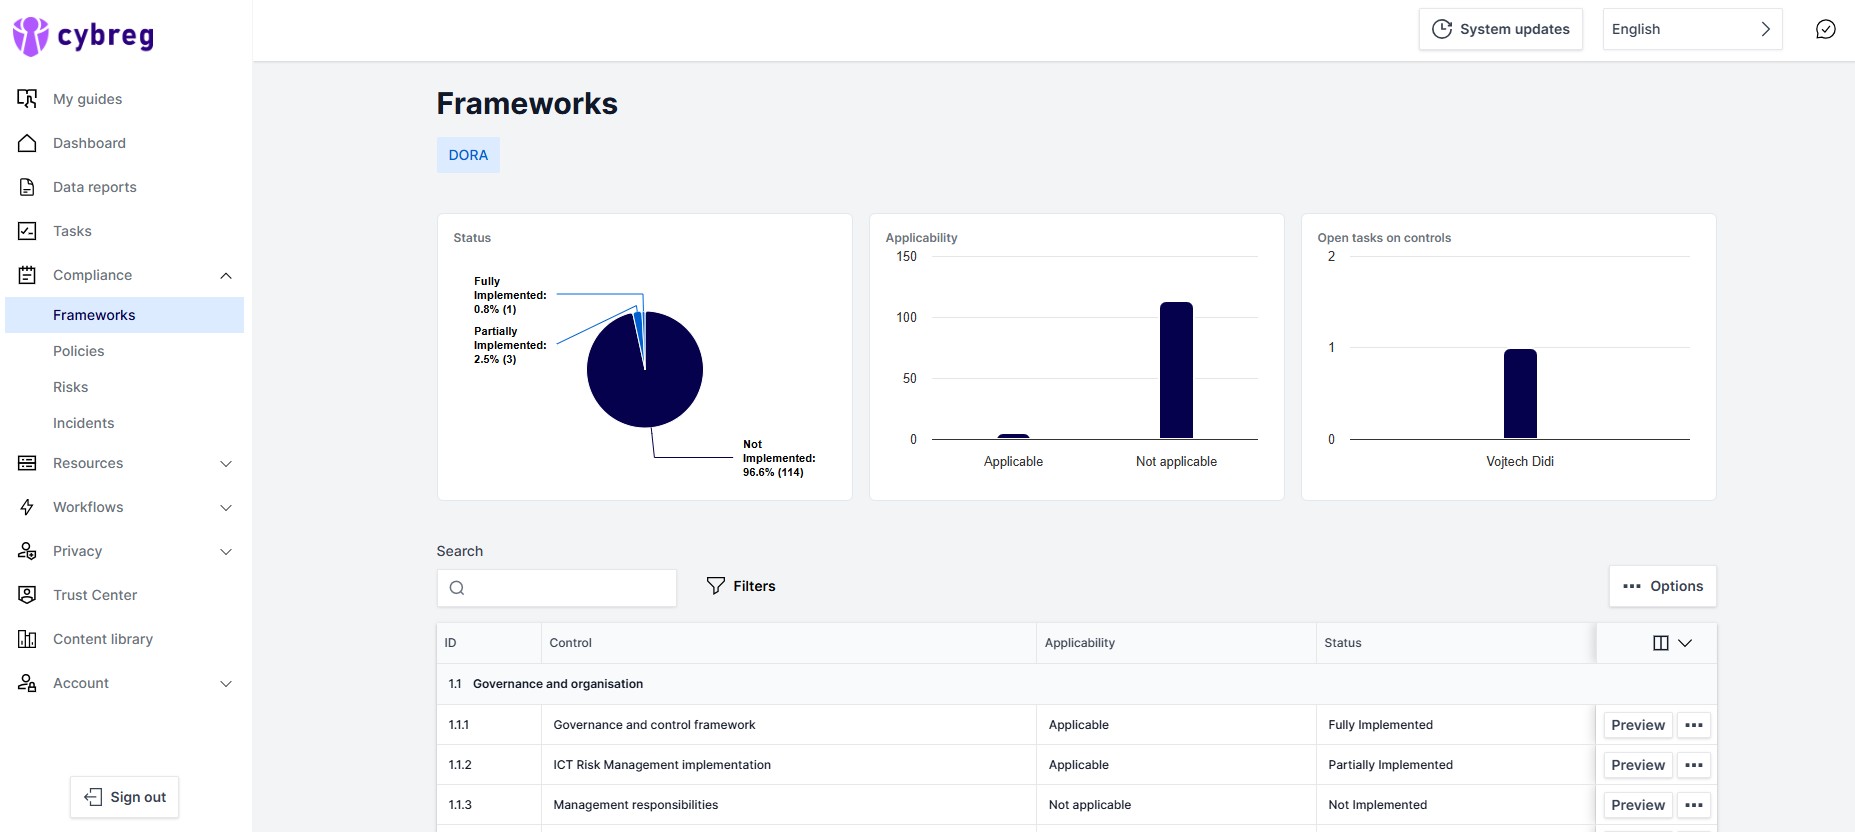
Translate regulatory requirements and standards into specific actions, responsibilities, and tasks. Track the status of implementation, assign owners, and link common actions across multiple regulatory frameworks.

Track and assess information, cyber, ICT, supplier, and operational risks. Establish your own methodology, risk matrices, and methods for calculating inherent, residual, or target risk. Corrective actions and tasks remain directly linked to the risk they address.
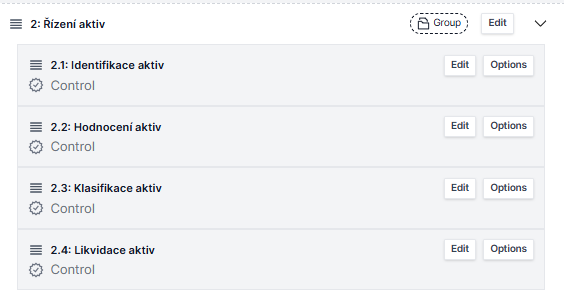
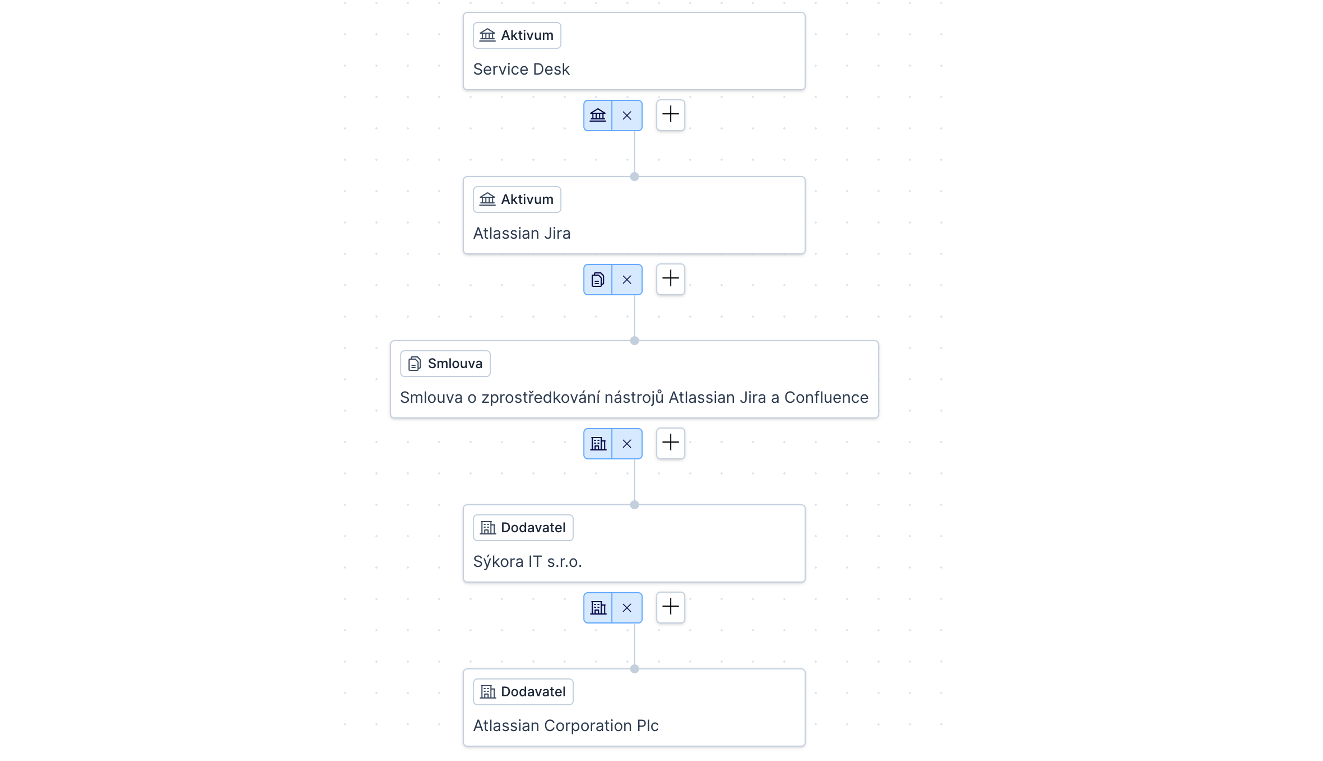
Manage information and ICT assets, systems, applications, business processes, and key functions. Track owners, responsibilities, criticality, and interdependencies so you can see how a change or incident might affect the rest of the organization.
Keep security policies and other documentation in a single, controlled environment. Version control, approval workflows, document distribution, and records of employee acknowledgments help minimize outdated documents and the need to manually search for documents.
A single piece of evidence can be used for multiple measures or regulatory requirements without having to upload and manage it repeatedly.
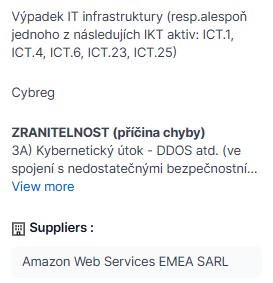
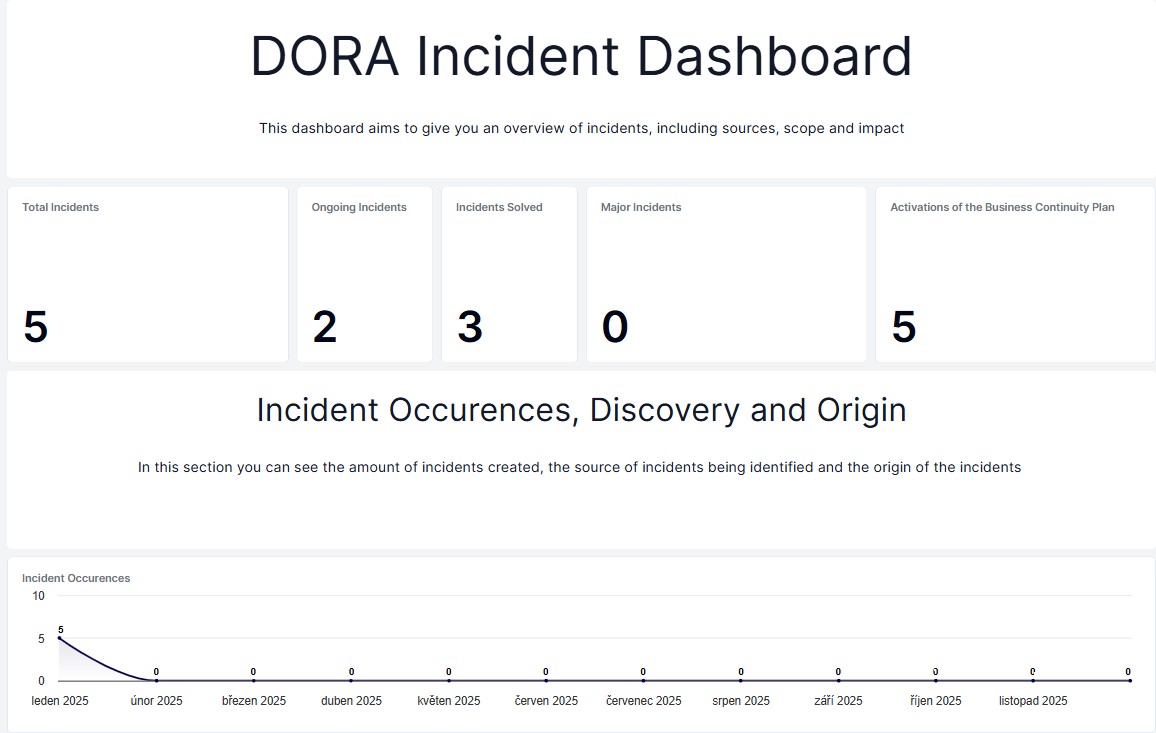
Record security events and incidents, assign responsibilities, track deadlines, and document the resolution process. Incidents can be linked to the affected assets, systems, vendors, processes, and risks.
The platform also supports business continuity management, business impact analysis, recovery plans, and records of readiness testing.
Create a centralized database of suppliers, services provided, contracts, evaluations, and related risks. Automate the distribution of questionnaires, periodic supplier reviews, the evaluation of responses, and the collection of documentation.
Convert requirements into specific tasks with an assigned owner and deadline. Automate regular reviews, approvals, comments, escalations, questionnaires, or recurring evaluations.
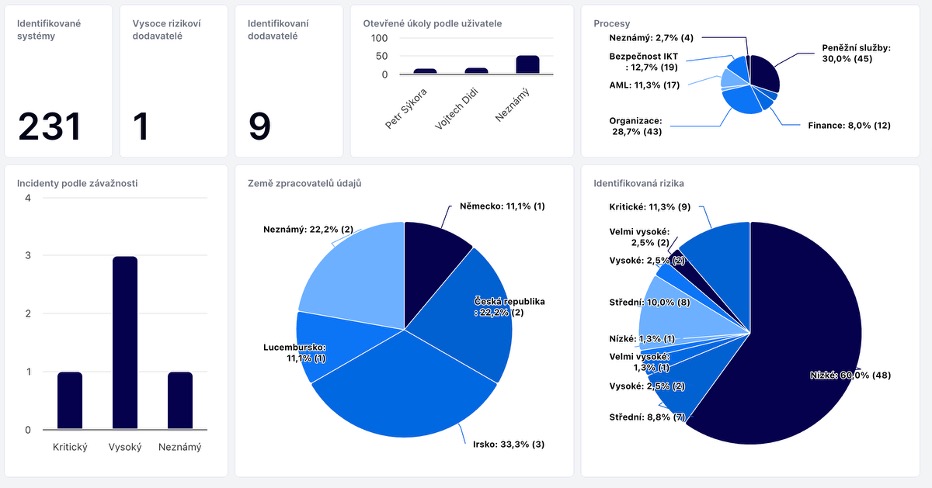
Create reports tailored to the needs of management, process owners, the security team, or auditors. Dashboards can display the status of implementation, open risks, deadlines, corrective actions, incidents, or the results of supplier audits.
A Growing Ecosystem of Packages for Various Standards
Marketplace allows you to expand the platform with pre-built compliance packages for specific regulations and standards. A package may include a structure of requirements, control measures, policies, sample risks, recurring tasks, and other content necessary for implementing the given framework.
Many of the requirements of DORA, NIS2/ZKB, ISO 27001, and other frameworks overlap. Therefore, you do not need to record the same asset, risk, policy, vendor assessment, or evidence multiple times. The platform allows you to link common measures across individual frameworks. When adding another regulation, you don’t start from scratch, but rather leverage your existing processes, responsibilities, and evidence.
Management of ICT risks, information and ICT assets, suppliers, incidents, the information registry, and regulatory reporting.
Asset inventory, risk analysis, security measures, Statement of Applicability, incidents, suppliers, and ongoing audit readiness.
Risk management for digital products, vulnerabilities, security requirements, corrective actions, and related documentation throughout the entire product lifecycle.
Management of the ISMS, control measures, security policies, risks, internal audits, corrective actions, and evidence.
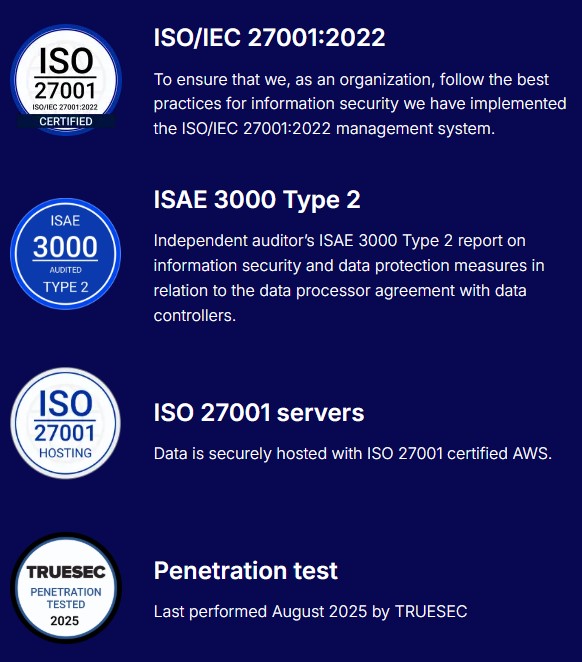
Platform security backed by international certifications
Learn more about product safety and data protection at https://formalize.com/en/security.
We’ll help you define the scope of the solution, data structure, roles and responsibilities, risk management methodology, workflows, and reporting. We’ll customize the platform to fit your environment, assist with importing existing data, and train your users.
We’ll guide you through the platform setup and help you translate the requirements of the selected regulation or standard into specific processes. We’ll configure roles, responsibilities, workflows, and data structures according to your organization’s needs.
As part of the CISO as a Service offering, an experienced external CISO can take charge of governance, risk management, incident management, vendor management, documentation, and audit readiness. The platform serves as a shared workspace for managing all these areas.
Everything you need to know about the Formalize platform for compliance and risk management.
The Formalize platform is a software environment for managing governance, risk, compliance, and cybersecurity. It links regulatory requirements to assets, risks, suppliers, policies, tasks, incidents, and evidence.
Yes. The Formalize platform offers a 14-day free trial (no credit card required). If you’d like to explore the platform’s features and cybreg’s Czech-language packages first, try the platform for free.
The platform will be used by cybersecurity managers, compliance specialists, auditors, and consultants. It supports organizations that are just beginning to implement their processes, as well as companies that coordinate multiple teams and regulatory frameworks.
No. The Formalize platform allows you to manage multiple regulatory, certification, and internal frameworks. The Formalize Marketplace offers a range of ready-made packages for various regulations and standards from Formalize and its partners.
Yes. Joint measures, policies, or evidence can be linked to multiple regulatory frameworks, which reduces duplicate record-keeping and the need to repeat the same activities.
Yes. You can configure custom fields, views, risk methodologies, forms, workflows, roles, dashboards, and reporting.
The cybreg team will help you set up the platform, import data, and train users. We also prepare and manage Czech regulatory packages that translate requirements into specific measures, sample documentation, and workflows. We’ll tailor the scope of our implementation support to your organization’s needs.
The platform provides the technological environment and framework for managing the agenda. As part of the CISO as a Service offering, an external expert also handles day-to-day management, coordination, expert decision-making, and reporting.
When it becomes difficult to keep track of requirements, responsibilities, and deadlines across spreadsheets and documents, Formalize links related information and helps manage compliance on an ongoing basis, including cross-team collaboration and the preparation of audit documentation.
The platform utilizes access control, data encryption, backup, monitoring, vulnerability management, and independent security audits. For more information, visit https://formalize.com/en/security.
Formalize allows you to add as many users as you need. You can onboard your own employees as well as external consultants or auditors to the platform and set the appropriate access permissions for them.